Türkiye’nin en büyük ve en bilinen cezaevi olan Silivri Cezaevi’nin adı değiştirildi. İstanbul Silivri Belediye Başkanı Volkan Yılmaz, ilçenin itibarına zarar verdiği gerekçesiyle Silivri Cezaevi’nin adının değiştirilmesi için cuma günü Adalet Bakanlığı’na başvurdu. Türkiye gazetesinin haberine göre; Yılmaz, dilekçesinde “Silivri denilince insanların aklına cezaevi geliyor. Bu da ilçemizin gelişmesini negatif yönde etkiliyor” ifadelerini kullandı. Başvuruyu değerlendiren Bakanlık, bu ismin Marmara Cezaevi olarak değiştirilmesini kararlaştırdı.
Tekrarlayan Düşük Nedir? İki ve daha fazla düşük yapılmasıdır. Kadınların yaklaşık %1’inde görülür. Üç ve daha fazla düşük yapılmış olması detaylı değerlendirmeyi gerektirir. Düşüklerin en sık görülen sebebi nedir? Düşüklerin çoğu (%60’ı) embriyonun oluşumu sırasında anormal sayıda kromozom almasından kaynaklanır. Bu tip genetik problem tesadüfen oluşur ve altta yatan bir tıbbi neden yoktur. Ancak ileri yaş gebelerde daha sık görülür. Gebelikte düşük hakkında bilgi almak için de gebelikte düşük çeşitleri sayfamızı ziyaret edebilirsiniz. Tekrarlayan düşüğe sebep olan başka genetik durumlar var mıdır? Bazı çiftlerde partnerlerden birinde translokasyon denen bir genetik bozukluk olabilir. Bu kromozomun bir parçasının koparak başka bir kromozoma yapışması durumudur. Translokasyon taşıyıcılarında herhangi bir fiziksel belirti olmaz. Ancak bazı yumurta ya da spermleri anormal kromozom taşır. Bu da embryonun az ya da fazla sayıda kromozoma sahip olmasına ve düşüğe sebep olur...
Ukrayna 'da direnişin sembolü haline gelen ve 40'tan fazla Rus uçağını düşürdüğü iddia edilen 'Kiev'in hayaleti' lakaplı efsane pilot Binbaşı Stepan Tarabalka'nın hayatını kaybettiği duyurulmuştu. Ancak bu gelişmeden günler sonra Ukrayna Hava Kuvvetleri şaşırtan bir açıklama yaparak "Kiev'in Hayaleti, karakteri Ukraynalılar tarafından oluşturulmuş bir süper kahraman efsanesidir" denildi. Efsanenin ise tek bir pilot değil, Kiev'in koruyan ekibin tamamı olduğu düşünülüyor. 6 Rusya ’nın Ukrayna’ya yönelik saldırıların ardından “Kiev’in Hayaleti” lakaplı Ukraynalı pilotun 29 yaşındaki Binbaşı Stepan Tarabalka olduğu açıklanmış ve 13 Mart’ta hayatını kaybettiği belirtilmişti. Yetkililer, tarafından Tarabalka’nın madalya ile onurlandırıldığını doğrulanmıştı. UKRAYNA HAVA KUVVETLERİ AÇIKLADI Ancak Rus ordusuna bağlı 40’a yakın savaş uçağını düşürdüğü öne sürülen “Kiev’in Hayaleti” lakaplı Ukraynalı pilotun gerçek olmadığı açıklandı. Ukrayna Hava Kuvve...
Tekrarlayan gebelik kayıplarının sebepleri ve tedavi yöntemleri nelerdir? Tekrarlayan gebelik nedir? Tıbbi adıyla “habituel abortus” sıklıkla gebelik sürecinin ilk üç ayında ve en az üç kere kayıpla tanımlanan bir durumdur. Yaklaşık olarak çiftlerin %2’sinde bu sorun görülmektedir. Bu kayıplar genellikle kromozomal ve genetik anormalliklerden kaynaklanır. Rahimde gözlenen anomaliler de gebelik kaybını tetikleyebilir. Düşük görülme oranı ise tüm anne adaylarında %20 oranındadır. Düşük gebelik riski ilerleyen yaşla ile birlikte artmaktadır. Düşük görülme olasılığı 24 yaş ve altında %9.5 iken, 30 yaş arasında %11 ve 40 yaş arasında ise %53’tür. Düşük belirtileri nelerdir? Herkesin bildiğinin tam tersi fiziksel egzersiz, yolculuk, cinsel aktivite, yürüyüş düşüğe neden olmamaktadır. Ciddi bir risk olmadığında bunlarda kısıtlama yapılması gerekmez. En sık karşılaşılan düşük belirtilerini şu şekilde sıralayabiliriz; – Vajinal kanamalar; vajinal kanama görüldüğü zaman hemen doktora başvurulm...
02.05.2022 02:34 | Son Güncelleme: 02.05.2022 02:45 Rusya Dışişleri Bakanı Sergey Lavrov'dan Ukrayna'da devam eden savaşla ilgili dikkat çeken bir açıklama geldi. Lavrov Ukrayna'daki operasyonlarını, İkinci Dünya Savaşı'nda Nazilere karşı kazandıkları zaferin yıl dönümü olan 9 Mayıs'ta bitirmek üzere hızlandırmayı hedeflemediklerini söyledi. Sergey Lavrov, İtalyan televizyon kanalı "Rete 4"te, Rusya-Ukrayna savaşına yönelik değerlendirmelerde bulundu. Lavrov, Rusya'nın Ukrayna'daki savaşı, İkinci Dünya Savaşı'nda Nazilere karşı zafer elde ettiği 9 Mayıs'ta bitireceğine dair çıkan haberlere ilişkin açıklama yaptı. "RUSYA HIZLANDIRMAYI AMAÇLAMIYOR" Çıkan haberleri yalanlayan Lavrov,"Rusya, Ukrayna'daki özel operasyonun tamamlanmasını, Nazizm'e karşı kazanılan 9 Mayıs Zafer Günü'ne kadar hızlandırmayı amaçlamıyor. Askerlerimiz eylemlerini belirli bir tarih üzerine yapay olarak uyarlamayacak. Ukrayna'daki ...
Tekrarlayan gebelik kayıplarının sebepleri ve tedavi yöntemleri nelerdir? Tekrarlayan gebelik kayıpları anne ve baba adayları için oldukça kötü bir durumdur. Tekrarlayan düşükler ile genellikle gebelik sürecinin ilk aylarında karşılaşılır. Kadın Hastalıkları, Doğum ve Tüp Bebek Uzmanı Op. Dr. Seval Taşdemir, konuyla ilgili önemli bilgiler paylaştı. Tekrarlayan gebelik nedir? Tıbbi adıyla “habituel abortus” sıklıkla gebelik sürecinin ilk üç ayında ve en az üç kere kayıpla tanımlanan bir durumdur. Yaklaşık olarak çiftlerin %2’sinde bu sorun görülmektedir. Bu kayıplar genellikle kromozomal ve genetik anormalliklerden kaynaklanır. Rahimde gözlenen anomaliler de gebelik kaybını tetikleyebilir. Düşük görülme oranı ise tüm anne adaylarında %20 oranındadır. Düşük gebelik riski ilerleyen yaşla ile birlikte artmaktadır. Düşük görülme olasılığı 24 yaş ve altında %9.5 iken, 30 yaş arasında %11 ve 40 yaş arasında ise %53’tür. Düşük belirtileri nelerdir? Herkesin bildiğinin tam tersi fiziksel egzers...
CK Yönetim kurulu Başkanı Gültekin Kaya'nın katılımıyla GÜNDEM TOKAT BU AKŞAM SAAT 18.00 DE TEMPO TV DE Tokat'a dair güncel haberler ile 16 Ekim Cumartesi günü bu akşam Saat 18.00 -20 arası Seyhan Güler ve Bayram Güvercin'in sunumuyla GÜNDEM TOKAT Haber programı TEMPO TV Ekranlarında olacak İZLEMEYİ UNUTMAYIN
Comments
#ticker-target, .ticker-content {
min-height: 40px !important; /* Bandın orijinal yüksekliği kaç ise o değeri yazın */
display: block;
overflow: hidden;
}
Updates about government-backed hacking and disinformation
byHaber D-
Updates about government-backed hacking and disinformation
Updates about government-backed hacking and disinformation The feed item title.
On any given day, Google's Threat Analysis Group (TAG) is tracking more than 270 targeted or government-backed attacker groups from more than 50 countries. Our team of analysts and security experts is focused on identifying and stopping issues like phishing campaigns, zero-day vulnerabilities and hacking against Google, our products and our users. Today, we’re sharing recent findings on government-backed phishing, threats and disinformation, as well as a new bulletin to share information about actions we take against accounts that we attribute to coordinated influence campaigns.
Hacking and phishing attempts
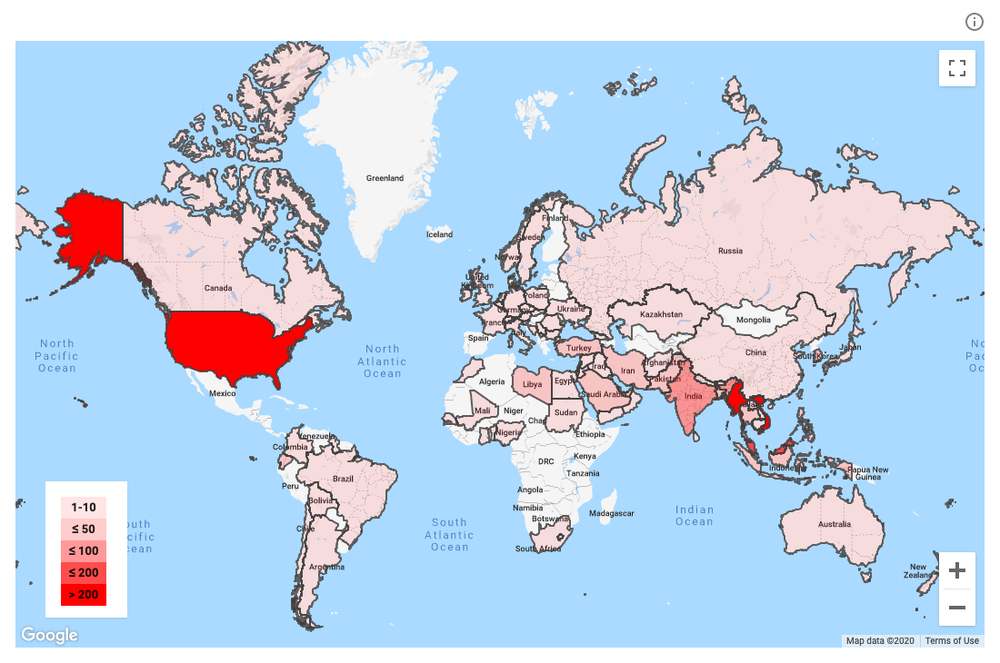
Last month, we sent 1,755 warnings to users whose accounts were targets of government-backed attackers.
Distribution of the targets of government-backed phishing attempts in April 2020
Generally, 2020 has been dominated by COVID-19. The pandemic has taken center stage in people’s everyday lives, in the international news media, and in the world of government-backed hacking. Recently, we shared information on numerous COVID-themed attacks discovered and confirmed by our teams. We continue to see attacks from groups like Charming Kitten on medical and healthcare professionals, including World Health Organization (WHO) employees. And as others have reported, we’re seeing a resurgence in COVID-related hacking and phishing attempts from numerous commercial and government-backed attackers.
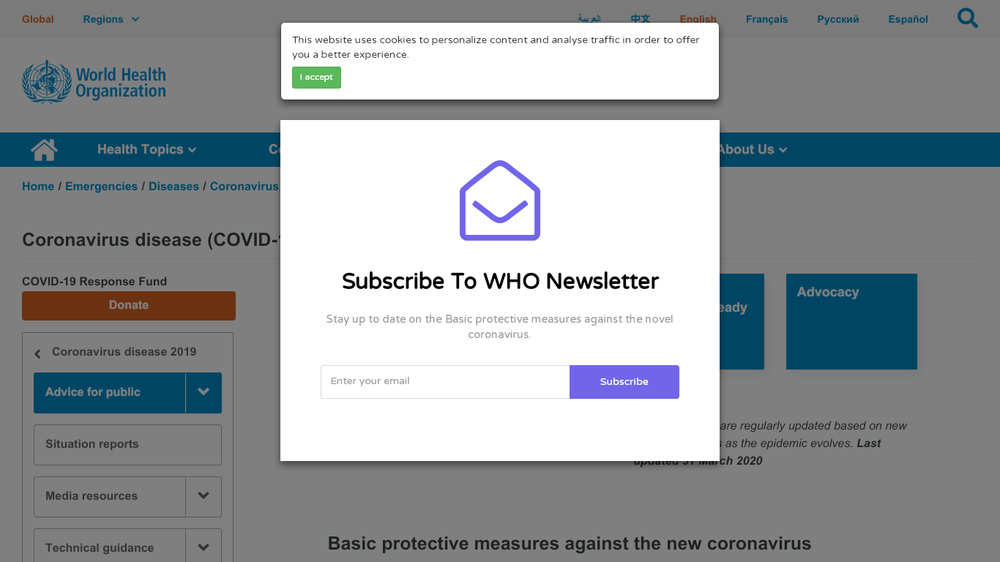
As one example, we've seen new activity from “hack-for-hire” firms, many based in India, that have been creating Gmail accounts spoofing the WHO. The accounts have largely targeted business leaders in financial services, consulting, and healthcare corporations within numerous countries including, the U.S., Slovenia, Canada, India, Bahrain, Cyprus, and the UK. The lures themselves encourage individuals to sign up for direct notifications from the WHO to stay informed of COVID-19 related announcements, and link to attacker-hosted websites that bear a strong resemblance to the official WHO website. The sites typically feature fake login pages that prompt potential victims to give up their Google account credentials, and occasionally encourage individuals to give up other personal information, such as their phone numbers.
Example of a spoofed WHO Newsletter sign-up prompt
To help protect users against these kinds of tracks, our Advanced Protection Program (APP) utilizes hardware security keys and provides the strongest protections available against phishing and account hijackings. APP was designed specifically for high-risk accounts.
Coordinated influence operations
Government-backed or state-sponsored groups have different goals in carrying out their attacks: Some are looking to collect intelligence or steal intellectual property; others are targeting dissidents or activists, or attempting to engage in coordinated influence operations and disinformation campaigns. Our products are designed with robust built-in security features, like Gmail protections against phishing and Safe Browsing in Chrome, but we still dedicate significant resources to developing new tools and technology to help identify, track and stop this kind of activity. In addition to our internal investigations, we work with law enforcement, industry partners, and third parties like specialized security firms to assess and share intelligence.
When we find attempts to conduct coordinated influence operations on our platforms, we work with our Trust & Safety teams to swiftly remove such content from our platforms and terminate these actors’ accounts. We take steps to prevent possible future attempts by the same actors, and routinely exchange information and share our findings with others in the industry. We’ve also shared occasional updates about this kind of activity, and today we’re introducing a more streamlined way of doing this via a new, quarterly bulletin to share information about actions we take against accounts that we attribute to coordinated influence campaigns (foreign and domestic). Our actions against coordinated influence operations from January, February and March can be found in the Q1 Bulletin.
Since March, we’ve removed more than a thousand YouTube channels that we believe to be part of a large campaign and that were behaving in a coordinated manner. These channels were mostly uploading spammy, non-political content, but a small subset posted primarily Chinese-language political content similar to the findings of a recent Graphika report. We’ll also share additional removal actions from April and May in the Q2 Bulletin.
Our hope is that this new bulletin helps others who are also working to track these groups, such as researchers studying this issue, and we hope these updates can help confirm findings from security firms and others in the industry. We will also continue to share more detailed analysis of vulnerabilities we find, phishing and malware campaigns that we see, and other interesting or noteworthy trends across this space.
The parsed post content.
On any given day, Google's Threat Analysis Group (TAG) is tracking more than 270 targeted or government-backed attacker groups from more than 50 countries. Our team of analysts and security experts is focused on identifying and stopping issues like phishing campaigns, zero-day vulnerabilities and hacking against Google, our products and our users. Today, we’re sharing recent findings on government-backed phishing, threats and disinformation, as well as a new bulletin to share information about actions we take against accounts that we attribute to coordinated influence campaigns.
Hacking and phishing attempts
Last month, we sent 1,755 warnings to users whose accounts were targets of government-backed attackers.
Distribution of the targets of government-backed phishing attempts in April 2020
Generally, 2020 has been dominated by COVID-19. The pandemic has taken center stage in people’s everyday lives, in the international news media, and in the world of government-backed hacking. Recently, we shared information on numerous COVID-themed attacks discovered and confirmed by our teams. We continue to see attacks from groups like Charming Kitten on medical and healthcare professionals, including World Health Organization (WHO) employees. And as others have reported, we’re seeing a resurgence in COVID-related hacking and phishing attempts from numerous commercial and government-backed attackers.
As one example, we've seen new activity from “hack-for-hire” firms, many based in India, that have been creating Gmail accounts spoofing the WHO. The accounts have largely targeted business leaders in financial services, consulting, and healthcare corporations within numerous countries including, the U.S., Slovenia, Canada, India, Bahrain, Cyprus, and the UK. The lures themselves encourage individuals to sign up for direct notifications from the WHO to stay informed of COVID-19 related announcements, and link to attacker-hosted websites that bear a strong resemblance to the official WHO website. The sites typically feature fake login pages that prompt potential victims to give up their Google account credentials, and occasionally encourage individuals to give up other personal information, such as their phone numbers.
Example of a spoofed WHO Newsletter sign-up prompt
To help protect users against these kinds of tracks, our Advanced Protection Program (APP) utilizes hardware security keys and provides the strongest protections available against phishing and account hijackings. APP was designed specifically for high-risk accounts.
Coordinated influence operations
Government-backed or state-sponsored groups have different goals in carrying out their attacks: Some are looking to collect intelligence or steal intellectual property; others are targeting dissidents or activists, or attempting to engage in coordinated influence operations and disinformation campaigns. Our products are designed with robust built-in security features, like Gmail protections against phishing and Safe Browsing in Chrome, but we still dedicate significant resources to developing new tools and technology to help identify, track and stop this kind of activity. In addition to our internal investigations, we work with law enforcement, industry partners, and third parties like specialized security firms to assess and share intelligence.
When we find attempts to conduct coordinated influence operations on our platforms, we work with our Trust & Safety teams to swiftly remove such content from our platforms and terminate these actors’ accounts. We take steps to prevent possible future attempts by the same actors, and routinely exchange information and share our findings with others in the industry. We’ve also shared occasional updates about this kind of activity, and today we’re introducing a more streamlined way of doing this via a new, quarterly bulletin to share information about actions we take against accounts that we attribute to coordinated influence campaigns (foreign and domestic). Our actions against coordinated influence operations from January, February and March can be found in the Q1 Bulletin.
Since March, we’ve removed more than a thousand YouTube channels that we believe to be part of a large campaign and that were behaving in a coordinated manner. These channels were mostly uploading spammy, non-political content, but a small subset posted primarily Chinese-language political content similar to the findings of a recent Graphika report. We’ll also share additional removal actions from April and May in the Q2 Bulletin.
Our hope is that this new bulletin helps others who are also working to track these groups, such as researchers studying this issue, and we hope these updates can help confirm findings from security firms and others in the industry. We will also continue to share more detailed analysis of vulnerabilities we find, phishing and malware campaigns that we see, and other interesting or noteworthy trends across this space.
The feed item description. Put the featured image on content. The feed item author. {authorlink} The feed item author link (If exist). https://www.blog.google/threat-analysis-group/updates-about-government-backed-hacking-and-disinformation/ The feed item permalink. https://www.blog.google/rss The feed URL. The Keyword The feed title.
The Keyword
The description of the feed. https://www.blog.google/static/blogv2/images/google.png The feed's logo image URL. BLOG GOOGLE This campaign title 687130 This campaign ID.
Templatesyard is a blogger resources site is a provider of high quality blogger template with premium looking layout and robust design. The main mission of templatesyard is to provide the best quality blogger templates which are professionally designed and perfectlly seo optimized to deliver best result for your blog.



 Hello, my name is Jack Sparrow. I'm a 50 year old self-employed Pirate from the Caribbean.